Configuration files
Give a service a file from your repository. It reads it at the path you choose.
compose.yaml
services:
  caddy:
    image: caddy:2
    configs:
      - source: caddyfile # (1)!
        target: /etc/caddy/Caddyfile # (2)!

configs:
  caddyfile:
    file: caddy/Caddyfile # (3)!
- The file this service may read.
- Where the service finds it.
- A file in your repository, in plain text.
Generated on every release. You never write these files or see them.
apiVersion: v1
data:
  content: ":80 {\n    reverse_proxy web:8000\n}\n" # (1)!
kind: ConfigMap
metadata:
  labels:
    com.docker.compose.project: my-app
  name: caddyfile
  namespace: my-app
- Your file, as text. A binary file travels as
binaryData.
apiVersion: apps/v1
kind: Deployment
metadata:
  labels:
    com.docker.compose.project: my-app
    com.docker.compose.service: caddy
  name: caddy
  namespace: my-app
spec:
  replicas: 1
  selector:
    matchLabels:
      com.docker.compose.project: my-app
      com.docker.compose.service: caddy
  strategy:
    type: Recreate
  template:
    metadata:
      annotations:
        checksum/configs: 45763d4691d7a9e3e75325550f14bddf2b791ce655e7c330ac4d8bc65ddb64cb # (1)!
      labels:
        com.docker.compose.project: my-app
        com.docker.compose.service: caddy
        com.docker.compose.network.default: 'true'
    spec:
      containers:
      - image: caddy:2
        imagePullPolicy: IfNotPresent
        name: caddy
        volumeMounts:
        - mountPath: /etc/caddy/Caddyfile # (2)!
          name: config-0
          readOnly: true
          subPath: content
      volumes:
      - configMap:
          items:
          - key: content
            mode: 292 # (3)!
            path: content
          name: caddyfile
        name: config-0
- Changes with the file. A new value restarts the service.
- Your
target. 0444: the file is read only.
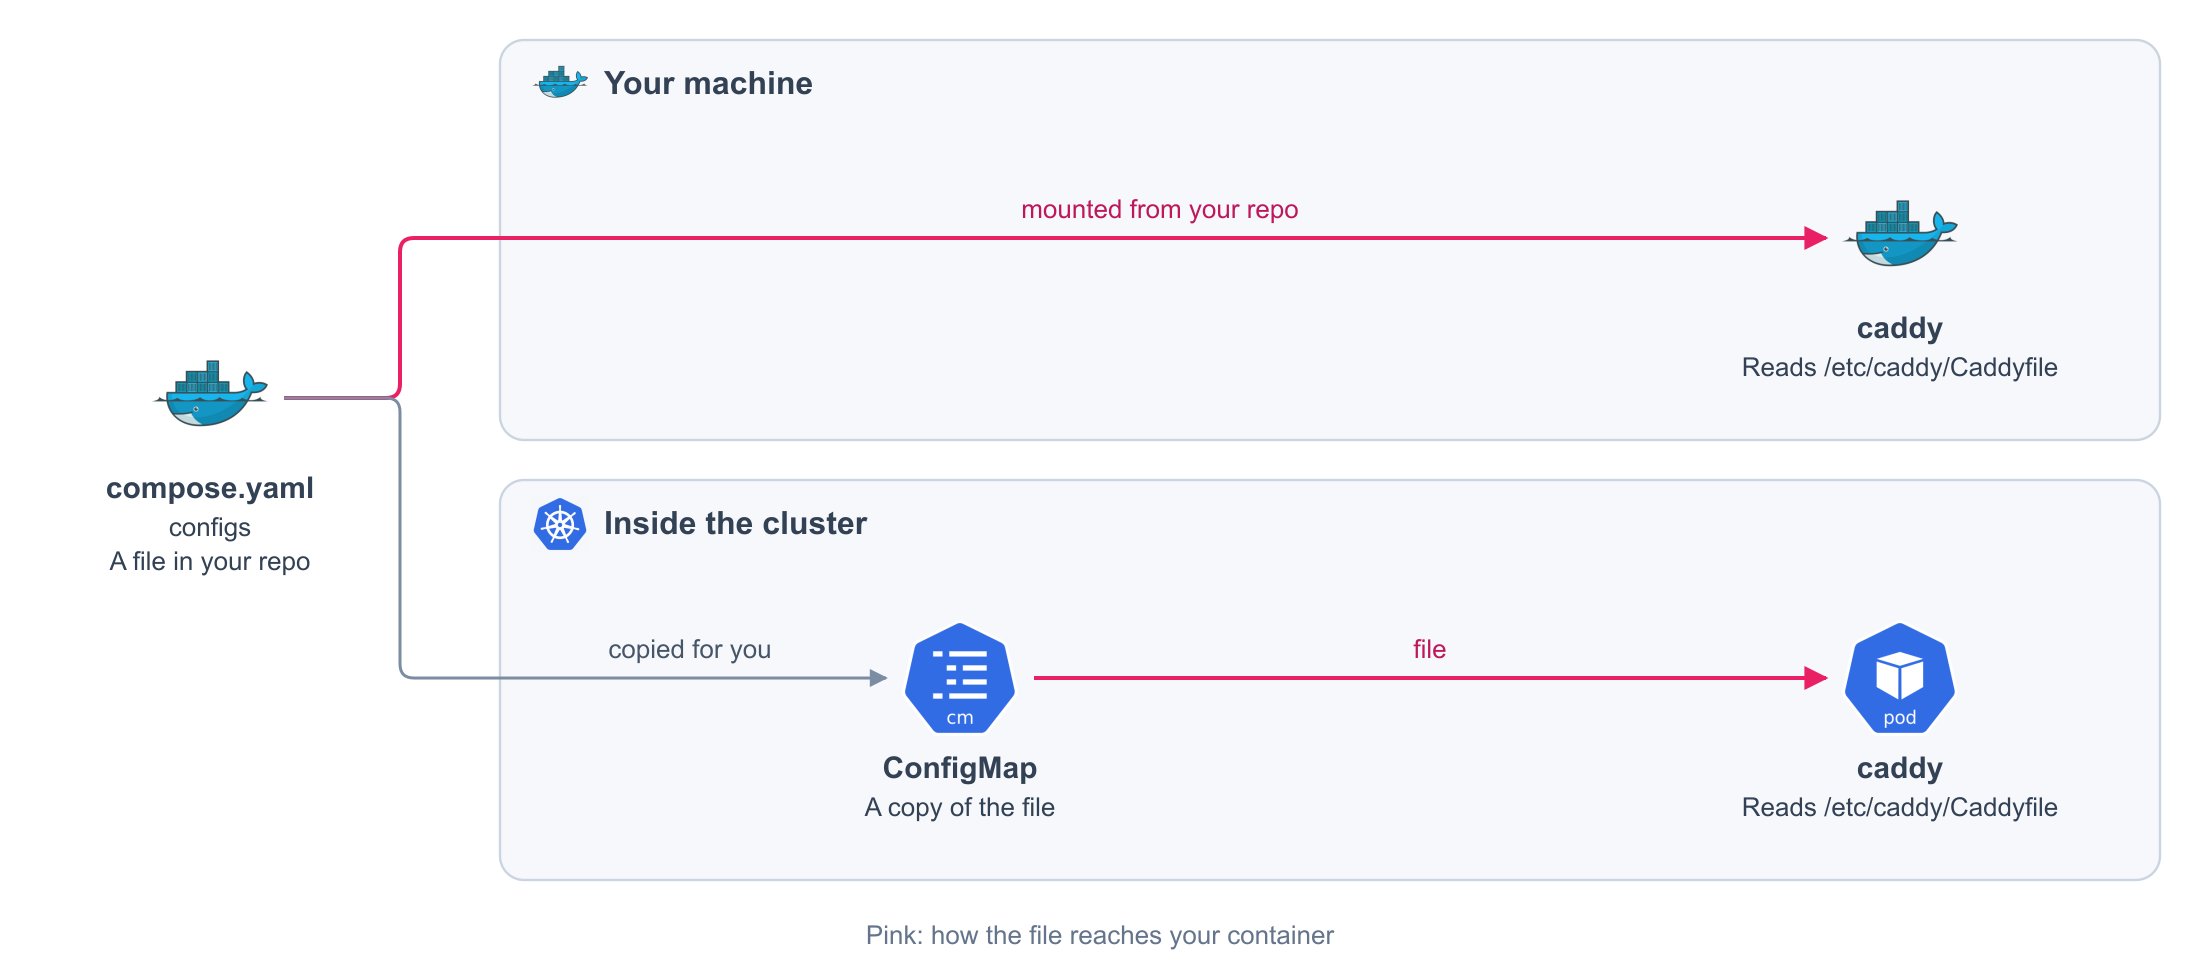
A config is for public files: a Caddyfile, a script, a logo. A credential goes in Secrets.
Fields
| Field | Required | Default | Values |
|---|---|---|---|
configs[].source |
Yes | The name of a config declared at the top | |
configs[].target |
No | /<source> |
An absolute path to the file inside the container |
configs[].mode |
No | 0444 |
Permissions of the file |
configs.<name>.file |
Yes | A file in your repository, text or binary |
What you get
On your machine
| Behavior | Detail |
|---|---|
| The file from your repository | Docker mounts it at target, read only |
| Edit and restart | Change the file in your repository and start the stack again |
On the cluster
| Behavior | Detail |
|---|---|
| A copy travels with the release | The file is read when the release is built |
| Read only | The service cannot change it |
| A change restarts the readers | A new content restarts the services that read the file, and no other |
Rules
| Rule | Detail |
|---|---|
| A config comes from a file | file is required. content and external are rejected |
| Up to 1 MiB | A bigger file is rejected |
| One file, one path | target is an absolute file path. Two files cannot share it, and a config cannot cover a secret |
| No owner per file | uid and gid other than 0 are rejected |